Search
Română
Magyar
English
Français
Deutsch
Italiano
Español
Русский
日本語
中国人
Change Language
Română
Magyar
English
Français
Deutsch
Italiano
Español
Русский
日本語
中国人
Sections
News
Exclusive
INSCOP Surveys
Podcast
EU
Diaspora
Republic of Moldova
Politics
Economy
Current Affairs
International
Sport
Health
Education
IT&C knowledge
Arts & Lifestyle
Opinions
Elections 2025
Environment
About Us
Contact
Privacy policy
Terms and conditions
Quickly scroll through news digests and see how they are covered in different publications!
News
Exclusive
INSCOP Surveys
Podcast
EU
Diaspora
Republic of Moldova
Politics
Economy
Current Affairs
International
Sport
Health
Education
IT&C knowledge
Arts & Lifestyle
Opinions
Elections 2025
Environment
52 events about "DNSC"
Yesterday 11:03
DNSC warns users / Fake Netflix messages attempt to steal card details
Current Affairs
2 November 2026, 19:40
The state could financially reward people who discover computer vulnerabilities in public institutions / The bill has passed the Senate and is heading to the Chamber of Deputies
Politics
28 October 2026, 08:36
Nearly 17,500 public institutions have been notified about the PHP2Shell cyber vulnerability, which may enable attacks and data theft
Current Affairs
19 October 2026, 12:52
The National Directorate for Cybersecurity is investigating a cyber incident at Radiocommunications
Current Affairs
4 October 2026, 19:08
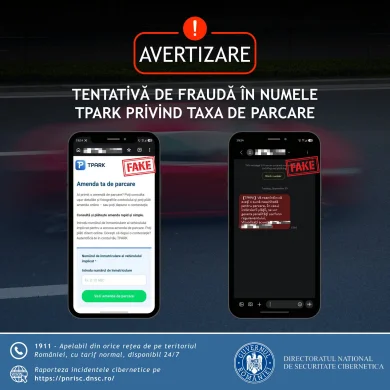
DNSC warns TPARK users: Fake messages demand urgent payment of alleged parking fines
Current Affairs
30 September 2026, 13:38
DNSC imposes a 50,000-lei fine on a central public institution for failing to report an incident on time
Current Affairs
27 September 2026, 18:21
DNSC warns: Fake websites imitate well-known brands to obtain personal and banking data
Current Affairs
16 September 2026, 14:06
PADROM warns about phishing attempts requesting personal data to verify the PAD policy
Current Affairs
9 September 2026, 19:15
Parliamentary Hearings: The National Cyberint Center Sent 1,300 Notifications Regarding Public Institutions’ Vulnerabilities
Current Affairs
9 September 2026, 17:44
The National Cyberint Center on the attack against ANCPI: the institution had been warned since 2021, but it did not provide an official response
Current Affairs
8 September 2026, 17:47
DNSC reported temporary difficulties accessing its website, possibly caused by a DDoS attack
Current Affairs
10 August 2026, 09:21
Methods by which you can protect yourself from the increasingly common frauds promoted by scammers, via WhatsApp
Current Affairs
1 August 2026, 16:26
The National Cyber Security Directorate draws attention to a method of fraud that uses Facebook groups to promote fake loans.
Current Affairs
30 July 2026, 14:45
DNSC warns about a campaign of fraudulent messages with false parking and speeding fines, sent in the name of Ghișeul.ro
Current Affairs
29 July 2026, 18:15
Dan Câmpean, the head of DNSC, announced that the ransomware attack on the National Administration of Penitentiaries is likely carried out by the Babuk group.
Current Affairs
27 July 2026, 17:21
DNSC warns about attempts of fraud via SMS that announce false parking fees / The messages request sensitive data through fraudulent links
Current Affairs
24 July 2026, 16:09
DNSC warns about the risks of free Wi-Fi networks in cafes, airports, and hotels
Current Affairs
21 July 2026, 13:24
DNSC warns: Fraudulent SMS campaign for false fines / Messages contain dangerous links
Current Affairs
15 July 2026, 14:23
DNSC warns about a clone of the Ghișeul.ro platform used for stealing personal and banking data
Current Affairs
7 July 2026, 16:09
DNSC Warning: The identity of the interim Minister of Finance, Alexandru Nazare, used in cyber frauds
Current Affairs
1
2
3
Editor’s Recommendations
Opinions
6 hours ago
Andrei Cornea: Democracy versus networks
Exclusive
12 hours ago
EXCLUSIVE | Romania, in the view of the Russian press: Ukraine’s “logistical rear”
Exclusive
6 hours ago
SPECIAL From Babasha to eMAG. "The bad manea" and "the useful manea"
Personalized news feed, AI-powered search, and notifications in a more interactive experience.