The DNSC warns that the North Korea-associated APT Lazarus group is using the ClickFix technique to compromise systems with malware, bypassing security measures.
Ana-Maria Tapescu


Current Affairs
Foto: pixabay.com

Always see our news on Google
The National Cyber Security Directorate (NCSD) has reported that APT Lazarus uses the ClickFix technique, which combines phishing with malicious command execution, to compromise targets. This method exploits user trust through fake web pages and job offers, causing victims to run malicious PowerShell commands. DNSC recommends training users, restricting PowerShell execution, blocking malicious domains, and implementing multi-factor authentication to mitigate risk.
Sources

Alertă transmisă de DNSC: APT Lazarus, grup asociat Coreei de Nord, exploatează tehnica ClickFix pentru distribuirea de malware / Este o ameninţare serioasă

ALERTĂ DNSC: APT Lazarus exploatează tehnica ClickFix pentru distribuirea de malware

Alertă - un grup asociat Coreei de Nord exploatează tehnica ClickFix pentru distribuirea de malware

Avertisment DNSC: Un grup asociat Coreei de Nord distribuie malware care fură informații și poate instala programe periculoase

Grupul APT Lazarus, asociat Coreei de Nord, distribuie malware prin exploatarea tehnicii ClickFix
Latest News
15:07
EU imposes stricter limits on electric cars
15:05
Six suspects were arrested in a human trafficking and pimping case
15:04
Storm Charles approaches Romania / ANM announces rain and strong gusts in the western and central parts of the country
15:04
The Ebola epidemic in Congo has caused 11,042 cases and 5,387 deaths
15:03
The German military is abandoning Chinese-made drones amid security risks and fears of espionage
See more news
NEWS ON THE SAME TOPICS
.webp)
Current Affairs
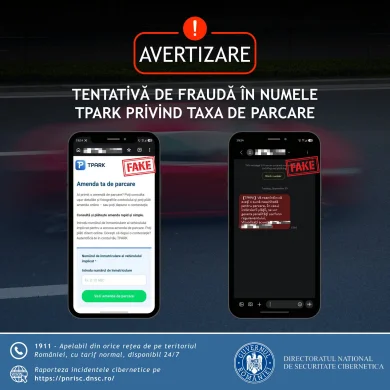
DNSC warns TPARK users: Fake messages demand urgent payment of alleged parking fines
Current Affairs
DNSC reported temporary difficulties accessing its website, possibly caused by a DDoS attack

Personalized news feed, AI-powered search, and notifications in a more interactive experience.


 (1).webp)