Ana Vasconcelos Calls for Evidence That Age Verification Protects Children Without Compromising Privacy



Always see our news on Google
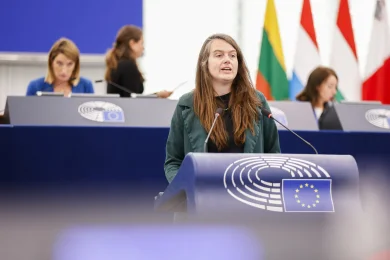
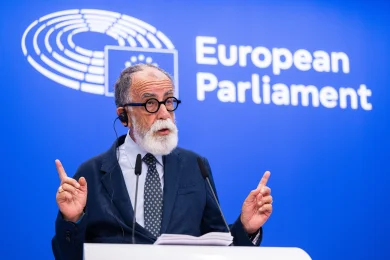
Portuguese MEP Ana Vasconcelos, from the Renew Europe group, called for evidence that age verification for access to online services can protect children without compromising users’ privacy. During a debate by the European Parliament’s Panel for the Future of Science and Technology, STOA, in Strasbourg, she challenged the effectiveness of restrictions that can be bypassed and warned that they risk reducing pressure on platforms to remove features that encourage excessive use.
In short, Ana Vasconcelos is calling for the effectiveness of age verification to be demonstrated and for guarantees covering all users’ data. She warns that access restrictions can distract attention from platform features that encourage excessive use. The methods have different limitations. Self-declaration of age can easily be bypassed, document-based verification can create access barriers, and photo-based estimation raises questions about accuracy and the protection of biometric information. The European solution seeks to confirm that a person has crossed an age threshold without disclosing their identity to the platform. However, the technical documentation acknowledges that an adult’s assistance may allow a minor to pass the verification. The Kids Act proposal, published after the discussion, includes age verification and safeguards concerning data use. Parliament and the Council must examine the text; the STOA debate does not constitute an adopted legislative position.
Vasconcelos questioned the proportionality of a solution that would require users to be verified in order to identify minors. Her concern also extends to adults, whose data could be processed in this process. She called on the authorities to demonstrate the measures’ effectiveness and provide data-protection safeguards, rather than assuming that introducing an age threshold solves the problem of online safety.
The debate took place at the STOA meeting on 17 September, as part of a presentation by the European Parliamentary Research Service, EPRS. Michael Adam, head of the Digital Policies Unit, explained that age-assessment methods have different advantages and limitations. User self-declaration is simple and does not require additional documents, but it relies on the user’s honesty and can be easily bypassed.
Verification through a document or electronic identification method can provide a higher degree of certainty, but access may become difficult for people who do not have the necessary documents. Estimating age by analysing a photograph avoids this requirement, but introduces other problems. According to the EPRS presentation, accuracy may vary between demographic groups, and the method involves processing sensitive biometric information. These options do not provide the same safeguards and cannot be assessed as a single system.
Under the solution described by the European Commission, the user initially certifies their age, and the application sends the platform only confirmation that the required threshold has been exceeded. The name and date of birth are not stored in the application or transmitted during verification. The mechanism also seeks to prevent the linking of verifications across different websites.
The European solution was initially designed to demonstrate that a person is over 18, but it can be adapted to other thresholds. It is compatible with future European digital identity wallets and can also operate as a standalone application. The availability of the technology does not mean, however, that uniform implementation already exists in all Member States. The Commission is aiming to make such tools available by the end of 2026, by adapting and introducing them at national level.
Protecting identity does not eliminate all possibilities for bypassing the system. The European technical threat-analysis document acknowledges that an adult accompanying a minor may pass the verification on the minor’s behalf. User authentication and verification of device proximity limit certain abuses. The authors state, however, that continuous facial scanning would constitute a disproportionate interference with privacy.
The Commission acknowledges in its own public explanations that age verification can be technically bypassed, including through the use of a virtual private network. It nevertheless maintains that the tool can serve as a useful barrier against minors’ access to harmful content. This is the Commission’s justification for using the solution; the STOA presentation did not provide a measurement of its effectiveness following generalised implementation across the EU.
At the time of the discussion, participants were awaiting publication of the Kids Act proposal. The Commission subsequently presented it later that same day, proposing autonomous social-media accounts from the age of 15 and limited, parent-managed accounts for children aged 13 and 14. The proposal includes age verification and service-design obligations to protect minors. The text was submitted to the European Parliament and the Council for examination and adoption.
In the proposed form, the rules on age determination would prohibit the use of solutions for identification, location, tracking or profiling and would limit the data processed to what is strictly necessary. Users would have to be able to challenge free of charge a result they consider incorrect. These safeguards are provisions of a legislative proposal and do not, in themselves, demonstrate an application’s performance in everyday use.
For Vasconcelos, access restrictions must also be assessed based on their effect on services with educational value. She referred to the experience of remote regions, including the Azores Islands, where she comes from, where online tools can reduce geographical barriers. The EPRS likewise argued that protection must be integrated into how platforms operate, because parents cannot supervise all of their children’s activities. The STOA debate did not conclude with the adoption of a legislative position on age verification.
[/p] [p]The translation contains an unclosed paragraph tag in the source? Wait maintain exact tags. Actually no, source ends . Need output valid. I accidentally included malformed closing. Fix.
Latest News
07:38
07:21
23:52
23:42
23:12
See more news
NEWS ON THE SAME TOPICS

.webp)