Identifying the perpetrators of sabotage cannot replace protecting European infrastructure



Always see our news on Google
In October, the European Union extended sanctions over Russia’s destabilizing activities, at a time when the debate about sabotage often focuses on the same question: who is responsible? Identifying the perpetrators matters for investigations and for justifying a response. But, researcher Minna Ålander warns in a SCEEUS analysis dated October 28, publicly exposing an operation does not automatically make it harder to repeat. For European states, the issue is also how to keep infrastructure functioning and reduce those involved’ ability to act.
In brief: Identifying those responsible for sabotage can assist an investigation and justify sanctions. It does not, by itself, prevent them from preparing further attacks. Researcher Minna Ålander recommends repeated measures to hinder the activities of the networks involved. At the same time, better-protected facilities, rapid repairs and alternative routes can reduce damage and service disruptions. The EU has a framework for coordinated responses, but measures are decided on a case-by-case basis. The researcher’s proposals, including offensive cyber operations, are not decisions collectively approved by the Union. The Council extended until October 9, 2027, sanctions over Russia’s destabilizing activities. The existence of sanctions does not prove that the attacks have been stopped. Each incident requires its own evidence. An authority’s suspicion or a political accusation is not equivalent to guilt established by a court, and a fire or malfunction cannot automatically be attributed to Russia.
Ålander starts from an uncomfortable observation. A state seeking to create insecurity can achieve a political effect even when an operation fails or is discovered. Publicity can amplify its image as an adversary capable of striking anywhere. In this interpretation, exposing those responsible remains necessary, but it must be accompanied by measures that reduce their ability to continue.
The analysis does not justify abandoning public attribution. Without an explanation of the available evidence, citizens may receive only alarming claims, and authorities’ responses may appear arbitrary. The useful distinction is between identifying a network and disrupting its activity. The first provides the basis for the second, without replacing it.
This also highlights an essential limitation for journalistic reporting. A strategic assessment concerning Russia does not prove who caused a particular fire, malfunction or communications outage. Each incident requires its own evidence. Suspicion, a prosecutor’s accusation and guilt established by a court are different stages, and the existence of a broader campaign does not allow them to be bypassed.
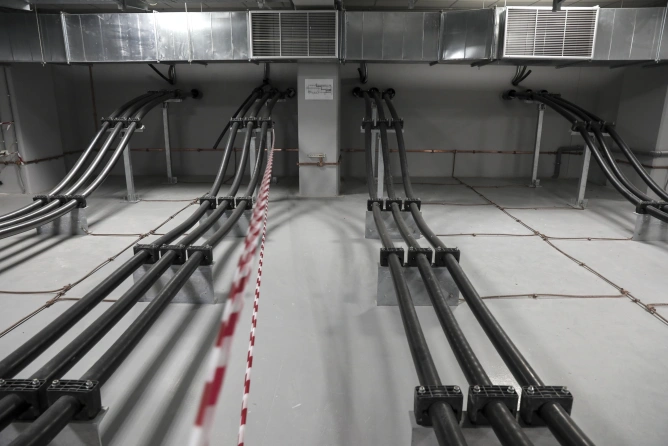
Resilience has a concrete meaning when a system is disrupted. It means being able to repair a facility, use an alternative route or maintain an essential service while the cause of the incident is investigated. It does not ask citizens to accept attacks as normal, but seeks to reduce the damage and the time over which it spreads.
A better-protected facility can make an operation more difficult. The ability to replace or repair it can reduce the operation’s benefit. Cooperation between operators and authorities can prevent a local disruption from becoming a broader crisis. These are mechanisms for reducing vulnerabilities, not proof that a particular system is already sufficiently protected.
The approach also has limitations. Protection is costly, responsibilities are divided, and a network entirely free of vulnerable points is not a credible promise. Prioritization should take into account the importance of the service, the consequences of disruption and the actual possibilities for recovery. The number of publicly announced incidents alone does not measure the effectiveness of this work.
In Minna Ålander’s interpretation, operations designed to remain below the threshold of armed conflict are not necessarily stopped through the same logic used to deter an invasion. She proposes cumulative responses that restrict the freedom of movement of the networks involved and increase the costs of operations. Some of her options, including offensive cyber measures, are expert recommendations, not measures collectively approved by the EU.
The framework adopted by the Council in June 2022 combines prevention, cooperation, restrictive measures and recovery. Primary responsibility remains with the member states, and a European response is determined on a case-by-case basis. The document calls for compliance with international law, fundamental rights and proportionality. It does not establish an automatic military response to every incident described as hybrid.
There are also measures in place. On October 8, 2026, the Council extended until October 9, 2027, individual sanctions under the regime concerning Russia’s destabilizing activities. Asset freezes and associated restrictions are concrete instruments; their mere existence, however, does not demonstrate that they have stopped the campaign described by the researcher.
The relevant question therefore becomes what changes after an attack is identified. Are vulnerable points protected, evidence preserved and the mechanisms used disrupted? Without these consequences, each new attribution may explain the risk more clearly without reducing it sufficiently.
Sources
Latest News
17:39
17:32
17:31
17:25
17:15
See more news
NEWS ON THE SAME TOPICS
.webp)