Commission opens infringement procedure against Romania over deficiencies in ship and port security controls



Always see our news on Google
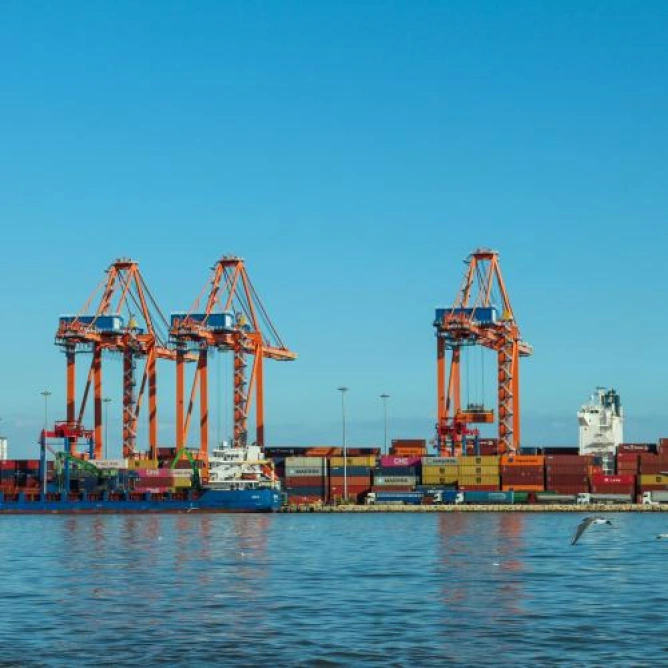
On Thursday, 19 November 2026, the European Commission opened an infringement procedure against Romania for failing to fulfill certain administrative and control obligations concerning the security of commercial ships, port facilities, and ports. The European executive considers that the Romanian authorities are not fully applying the framework intended to prevent intentional unlawful acts, including organized crime and illicit trafficking, and to protect critical infrastructure. The procedure, registered under number INFR(2026)2252, begins with a letter of formal notice, and Romania has two months to respond. The Commission has not publicly specified which ports or which individual obligations are concerned.
In brief On 19 November 2026, the European Commission opened procedure INFR(2026)2252 against Romania by sending a letter of formal notice. The case concerns administrative and control tasks relating to the security of commercial ships, port facilities, and ports. The Commission has not publicly identified any ports, operators, or individual deficiencies. The rules seek protection against intentional unlawful acts, including unauthorized access and illicit trafficking. They require security assessments, protection plans, controls, and inspections, distinct from the prevention of navigation accidents. Romania has two months to respond and remedy the shortcomings. If the response is unsatisfactory, the Commission may issue a reasoned opinion; in this case, it has not announced a referral to the CJEU or a financial penalty.
In its 19 November communication, the Commission cites three legislative acts: Regulation (EC) No 725/2004, Directive 2005/65/EC, and Regulation (EC) No 324/2008. These establish complementary obligations for protecting commercial ships, the facilities where ships interact with land-based infrastructure, and ports as a whole. The framework includes threat assessment, planning of protection measures, designation of responsibilities, and verification of implementation. These are general requirements of the legislation, not a list of the individual deficiencies attributed to Romania.
The procedure concerns protection against intentional unlawful acts, such as sabotage, unauthorized access, or illicit trafficking. In maritime terminology, this is the sphere of security, distinct from accident prevention and the technical safety of navigation. The Commission did not identify an attack, an unsafe ship, or a specific incident in its communication.
The first act cited by the Commission is Regulation (EC) No 725/2004, which introduces at EU level requirements based on the International Ship and Port Facility Security Code, known as the ISPS Code. It was developed within the International Maritime Organization in connection with the SOLAS Convention on the Safety of Life at Sea. The Regulation seeks to identify threats and establish measures to protect ships and port facilities involved in maritime transport. In this context, a port facility is the area where direct interactions between a ship and a port take place: the embarkation or disembarkation of persons, cargo handling, or the provision of services necessary for the ship.
The rules include security assessments, specific plans, designated responsibilities, and measures such as access control, monitoring of sensitive areas, and procedures for responding to threats. For ships, the ISPS framework also entails security plans, responsibilities at company and ship level, and appropriate certification.
Protecting a port facility is not sufficient if other areas of the port or the links between them remain outside a coordinated assessment. For this reason, Directive 2005/65/EC extends the approach to ports as a whole, taking into account the particularities of the infrastructure and the interactions between different sectors. The Directive requires Member States to designate authorities responsible for port security, conduct risk assessments, and ensure the preparation, approval, implementation, and updating of security plans. Assessments must identify important infrastructure and assets, possible threats, and vulnerabilities that could facilitate the occurrence of an incident.
The plans establish the procedures, measures, and responsibilities applicable depending on the level of risk. They must be coordinated with the plans of port facilities regulated by the ISPS framework. The Directive provides for three security levels: a basic level, one involving additional measures when the risk increases, and one for situations in which an incident is likely or imminent. Assessments and plans must be reviewed when necessary and at least once every five years. States are required to monitor the application of the plans and ensure that appropriate exercises are carried out.
The third act cited, Regulation (EC) No 324/2008, establishes the inspection procedures through which the European Commission verifies the implementation of legislation on maritime security. The purpose of these inspections is to enable verification of the compliance of national systems and procedures with European requirements. By its nature, the control is not limited to the existence of legislative acts. The verification may examine how competent authorities organize and supervise the application of security obligations. The European framework thus creates a link between protection requirements, the administrative responsibilities of states, and the Commission’s ability to verify whether these obligations function effectively.
In Romania, Government Decision No 248/2004 establishes the methodological rules for implementing the ISPS Code, while Order No 290/2007 of the Minister of Transport transposes the directive on port security. It assigns responsibilities to the Ministry of Transport and port security authorities, including the administrations of maritime ports, the maritime Danube ports, and navigable canals. The Romanian Naval Authority separately publishes the security and certification rules applicable to ships and port facilities. The existence of a national framework does not certify that all tasks are fulfilled in practice.
The Directive also requires cooperation between those responsible for the security of the entire port and the security officers of port facilities. A maritime operation may involve several areas and institutions, from the ship’s arrival to cargo handling and its departure from the port. Periodic exercises and checks seek to test the application of procedures when the threat level changes.
The letter of formal notice represents the first formal stage of the infringement procedure provided for by Article 258 of the Treaty on the Functioning of the European Union. Through this notification, the Commission informs the national authorities of its concerns regarding the application of European law and gives them the opportunity to respond. Romania has two months to submit explanations and remedy the deficiencies identified. If the responses are insufficient, the Commission may issue a reasoned opinion, setting out its legal position and requesting compliance. A possible referral to the Court of Justice represents a subsequent stage. On 19 November, the Commission had not announced a referral to the court, a judgment finding against Romania, or a financial penalty against Romania in this case. The response period runs from the official notification.
The Commission will assess the response of the Romanian authorities before deciding whether to close the case or continue the procedure.
Latest News
17:52
17:51
17:40
17:31
17:24
See more news
NEWS ON THE SAME TOPICS